SEC2009 Advancing Cybersecurity Through Research & Community

SEC2009

Advancing Cybersecurity Through Research & Community

Latest Articles

Technical Guides

Building an OSINT Capability: A Structured Approach for Threat Hunters and Security Researchers

Open-source intelligence has matured from an informal investigative technique into a structured discipline that complements — and often outpaces — traditional threat detection methods. This guide walks security practitioners through the tools, methodologies, and ethical frameworks required to build a functional OSINT program, from initial reconnaissance workflows to automated collection pipelines and responsible disclosure practices.
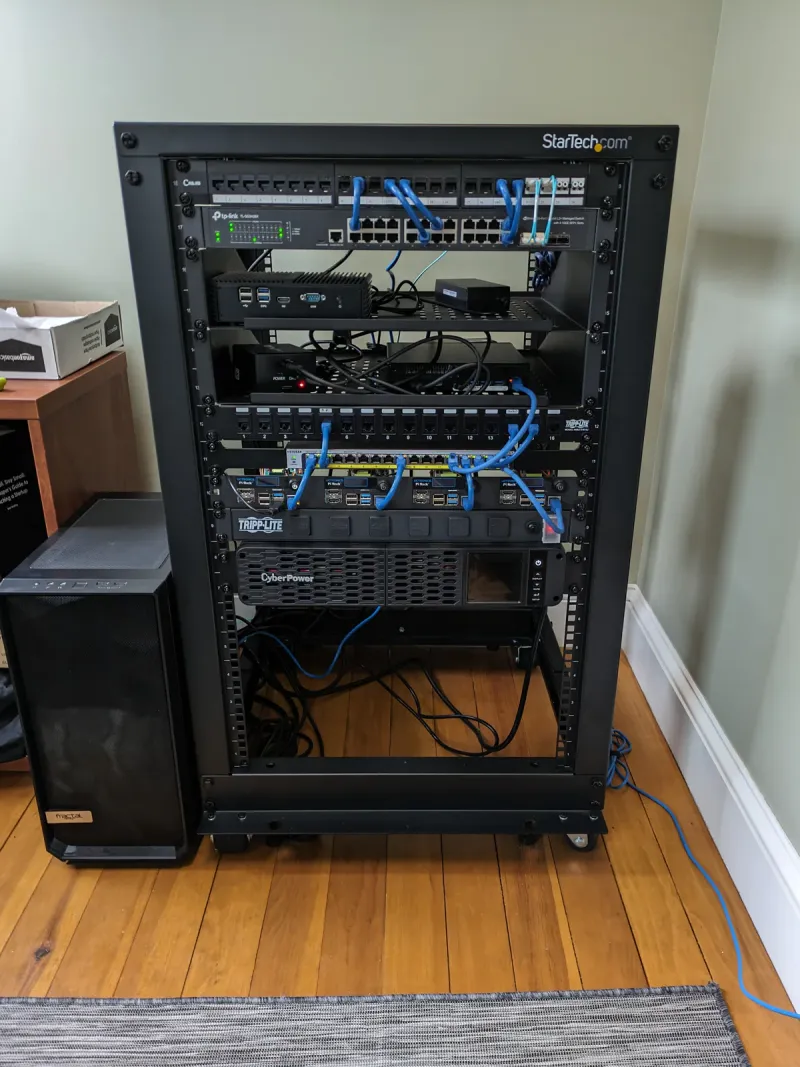
From Spare Parts to Security Research: A Practitioner's Guide to Building a Functional Lab Environment
Technical Guides

From Spare Parts to Security Research: A Practitioner's Guide to Building a Functional Lab Environment

Establishing a dedicated environment for vulnerability research and malware analysis is one of the most valuable investments a cybersecurity professional can make in their own development. Whether you are working from a spare bedroom or a dedicated organizational space, a well-architected lab enables hands-on experimentation that no certification course can replicate. This guide walks through hardware selection, virtualization strategy, essential open-source tooling, and the legal boundaries eve

Historical Analysis

Lessons Forged in Fire: How the Breach Era of 2009 Rewired Enterprise Cybersecurity Forever

The security incidents of 2009 were not isolated failures—they were a collective wake-up call that fundamentally reshaped how organizations defend their digital infrastructure. From the Heartland Payment Systems breach to the Conficker worm's peak propagation, that year produced a crucible of hard lessons still embedded in today's compliance frameworks and threat modeling methodologies. This retrospective examines what happened, why it mattered, and how those events continue to influence the dec